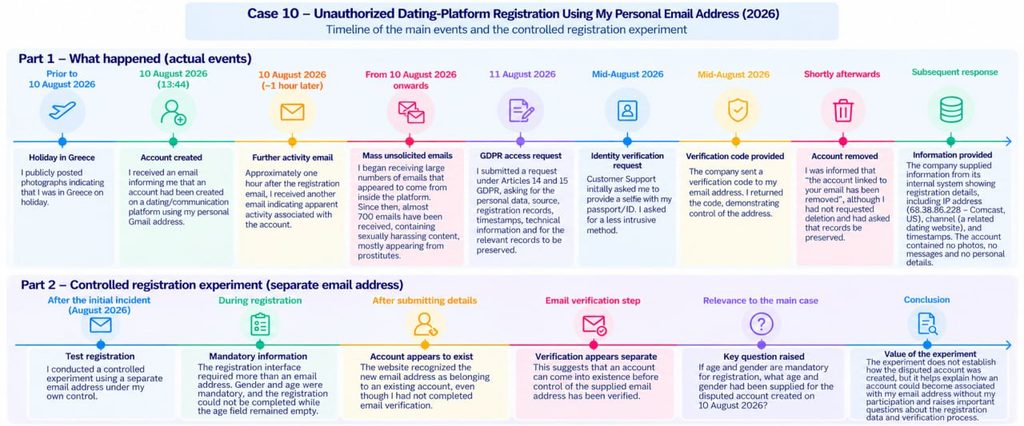
On 10 August 2026, I unexpectedly received an email informing me that an account had been created on a dating/communication platform using my personal Gmail address.
I had not created this account, had not initiated the registration, and had not authorized another person to use my email address for this purpose.
The timing was particularly striking to me. The registration occurred on the same day that I had publicly posted photographs indicating that I was in Greece on holiday. I record this fact as part of the chronology only. I have no evidence establishing that the public posts and the unauthorized registration were causally connected.
Approximately one hour after the account-creation notification, I received another email indicating apparent activity associated with the account.
This prompted me to investigate how my personal email address had entered the platform’s systems and what personal data had been associated with the registration.
Why the email address itself matters
The email address used for the registration was not my professional address but a personal Gmail address.
To the best of my current knowledge, this is not an address that I broadly publish online.
During my subsequent investigation, I was able to identify its historical appearance in connection with FORMEC: in material associated with a presentation on ResearchGate that had been deleted approximately two years earlier, and in FORMEC proceedings.
I do not presently know whether the person or system responsible for the registration obtained the address from either of these sources, from another source, or by some entirely different means.
This is one reason why the provenance and technical registration information retained by the platform is particularly important.
My GDPR access request
On 11 August 2026, I submitted a request under Articles 14 and 15 GDPR.
I asked for the personal data associated with the account, the source of my email address, registration records and timestamps, available technical information, verification status, profile visibility and activity, recipients of the data, and information about how the registration had been initiated.
Importantly, I expressly stated that I was not requesting deletion of the account records. Since I had not created the account myself, my priority was first to understand how the registration had occurred. I therefore also asked that relevant registration and technical records be preserved while my request was being examined.
Identity verification and removal of the account
Customer Support initially requested that I provide a selfie while holding my passport or identity document.
Because the entire problem concerned an account created without my authorization, I was reluctant to provide the platform with even more identifying information unless this was genuinely necessary.
I therefore asked whether control of the affected email address could be verified through a less intrusive method.
The company subsequently sent a verification code to the affected email address. I returned the code, thereby demonstrating control of the address.
Nevertheless, shortly afterwards I was informed:
“The account linked to your email has been removed.”
This concerned me because I had expressly stated that I was not requesting deletion of the underlying data and wanted the records preserved so that the circumstances of the registration could be established.
I therefore immediately requested preservation of any registration records, timestamps, source information, logs, profile information and records concerning removal of the account that still existed.
Customer Support subsequently confirmed that the verification code had in fact been sufficient to verify my control of the email address and that my GDPR request had been forwarded for further review.
What the internal records initially showed the company subsequently provided screenshots from its internal system.
The information supplied to me showed that the disputed registration was associated with:
IP address: 68.38.86.228 – Comcast Cable, United States
Channel: a related dating website
Sign-up: 10 August 2026, 13:44
Last time on site: 10 August 2026, 13:45
The company also stated that the account contained no photographs, videos, address or personal details and no messages sent or received. It described the account as an empty registration record and stated that nothing had been published in my name.
A controlled registration experiment
To better understand the registration mechanism, I conducted a controlled experiment using a completely separate email address under my own control.
The registration interface required more than an email address. Gender and age were mandatory, and the registration could not be completed while the mandatory age field remained empty.
At the same time, I observed that an account showedcould apparently come into existence before control of the supplied email address had been verified. In my controlled test, the website recognized the new email address as belonging to an existing account even though I had not completed email verification.
This experiment does not establish how the disputed account was created. It does, however, demonstrate why I asked how an account could have become associated with my personal email address without my participation.
It also raised an obvious question: if age and gender were mandatory, what age and gender had been supplied for the disputed account?
Automated emails that did not correspond to the account record
Although Customer Support told me that the disputed account contained no photographs and no messages sent or received, I had received emails presenting apparent activity involving other profiles.
During my controlled registration, I also received an automated notification claiming that another profile “likes your photos”.
Since this appeared difficult to reconcile with an account containing no photographs, I asked the company to explain the underlying system event rather than attempting to infer from the wording what had actually happened.
The company’s explanation: two system errors
On 21 August 2026, Customer Support provided an important clarification.
It stated that the branding appearing in certain emails had been an error in its email templates. According to the response, the disputed registration had actually been recorded through a related website belonging to the same operation, while the “Channel” designation represented an internal CRM field.
Customer Support acknowledged a second error concerning the apparent activity notifications.
According to its explanation, these were standard automated notifications generated by the system which should never have been sent to the disputed account. The company stated that the notifications had not been written by other users and that nothing had been sent from the account.
The company also acknowledged that the screenshots initially supplied to me had omitted the gender and age fields and provided updated screenshots.
The updated record showed:
Gender: Male
Age: 21
I did not provide either of those data.
A particularly important timestamp discrepancy
The updated screenshots also introduced what I consider one of the most important unresolved factual issues in this case.
The information available to me on 18 August 2026 showed:
Last time on site: 13:45 – 10 August 2026
Indeed, my correspondence of 18 August expressly referred back to that supplied record and asked the company to explain the timestamps and timezone.
However, in the updated information supplied on 21 August 2026, the account record instead showed:
Last time on site: 23:09 – 14 August 2026
I did not access the disputed account on 14 August.
This chronology creates an important factual question.
If the account had in fact been accessed or otherwise registered as active on 14 August, why did the information subsequently available to me on 18 August still identify 10 August as the “Last time on site”?
There may be a technical explanation — for example, the field may have been updated by an internal system event rather than an actual user login, or the earlier screenshot may itself have contained incomplete or erroneous information. I do not presently know.
For precisely that reason, I have asked the company to identify the event that caused the field to change, and, if retained, to provide the corresponding timestamp and timezone, IP address, user agent and event information.
This is not an allegation that the record was altered improperly. It is a documented inconsistency between information provided at different stages of the same investigation, for which I am seeking a technical explanation.
A second development occurring at the same time
There is another aspect of the chronology that I am documenting separately because I currently cannot establish whether it is connected to the unauthorized registration.
From the period following the creation of the disputed account, I began receiving an extraordinary volume of unsolicited emails containing heavily sexualized and pornographic material.
By 14 August, I had documented 28 such emails within approximately 16 hours. In my correspondence with Customer Support I expressly stated that I could not establish whether these emails were technically connected with the disputed account and did not attribute responsibility to the platform.
The phenomenon has continued.
At the time of writing, I am receiving approximately 50 unsolicited emails per day, many containing pornographic or heavily sexualized material. They frequently originate from new or changing sender accounts. I block them, but new senders continue to appear.
I am preserving these communications and their available technical information as evidence.
The temporal sequence is therefore noteworthy:
10 August 2026: I publicly indicated through photographs that I was in Greece on holiday.
10 August 2026: an account that I did not create was registered using my personal Gmail address.
Thereafter: I began experiencing a continuing high-volume stream of unsolicited sexualized/pornographic emails.
I emphasize that chronology is not proof of causation.
At present, I have no evidence demonstrating that the dating-platform registration caused the subsequent emails, that the platform disclosed my address to the senders, or that the public holiday posts were connected to either event.
I am documenting the sequence because it happened and because the technical evidence may eventually establish whether the events are related or entirely independent.
Registration wording concerning explicit communications and third-party sharing
During my controlled examination of the registration process, I also observed that the signup page stated that, by clicking the registration button, the user would agree not only to the platform’s terms and privacy policy, but also to receive sexually explicit communications and to the sharing of personal data with third-party partners.
This wording was particularly relevant to the disputed registration because I did not complete that registration or click the registration button myself.
I therefore asked the company to clarify whether any such consent was recorded in connection with the unauthorized account and, more importantly, whether any personal data associated with that particular registration were actually disclosed to third parties.
I do not presently know whether any such disclosure occurred.
Interestingly, in my separate controlled account — which I created myself but did not email-verify — I have not received a comparable stream of external emails. This does not prove that the two registrations were treated differently for any particular reason, but it provides a useful control observation when evaluating the disputed account.
What remains unresolved
At the time of writing, I still do not know:
- who or what submitted my personal Gmail address;
- where that person or system obtained it;
- why Male / 21 became associated with the account;
- whether the email address was ever verified during the original registration;
- what event produced the later 14 August “Last time on site” timestamp;
- why information available on 18 August still showed 10 August as the last activity if the later 14 August timestamp represented genuine earlier activity;
- what timezone the timestamps represent;
- what underlying events generated the automated activity notifications;
- whether any data associated with the registration were disclosed to third parties;
- whether there is any connection whatsoever between this registration and the subsequent wave of unsolicited sexualized emails; and
- what registration, consent, referral and provenance records still exist.
I have asked Customer Support to clarify the remaining factual questions before I regard my Article 15 access request as complete.
Why I am documenting this case
I am publishing this case primarily as a record of what can happen when an email address becomes associated with an online account that its owner did not create.
It also illustrates why email verification, accurate activity records, provenance information and meaningful GDPR access rights matter.
In this case, Customer Support has itself acknowledged errors concerning both the emails sent in connection with the account and information initially provided about the account. At the same time, the internal records contain profile attributes I did not provide and an activity timestamp that I cannot presently explain.
I am deliberately not identifying the companies involved in this public account, because my objective is not to publicly accuse a particular business or individual.
Nor am I claiming that the company created the unauthorized account, that it caused the subsequent unsolicited emails, or that any identifiable person was responsible.
My objective is to document the evidence, preserve the chronology, exercise my rights under the GDPR and allow the available technical records — rather than speculation — to establish what actually happened.
======================================================================== ==================================================
Further development: a second Article 15 request and an update to the Austrian Data Protection Authority
On 21 August 2026, I submitted a separate Article 15 GDPR access request concerning the controlled test account that I had created using a different email address under my own control.
This second request serves an important comparative purpose. Unlike the disputed account, I know exactly how the test account was created, which information I entered, which IP address I used, and which steps I did and did not perform. In particular, I deliberately did not complete the email-verification process.
I asked the operator to provide the personal data and technical registration information associated with this controlled account. Such information could help establish what records the platform normally generates and retains when an account is created but the supplied email address is never verified.
As of 22 September 2026, I have not received the requested Article 15 information concerning this controlled account, nor have I received a notification explaining an extension of the response period.
I have preserved the relevant registration information, the IP address used for the controlled registration, screenshots, and my correspondence concerning this request.
Update to the Austrian Data Protection Authority
On 22 September 2026, I submitted a further update to the Austrian Data Protection Authority concerning the case.
My original submission to the Authority had been made on 13 August 2026 after discovering the unauthorized registration and encountering difficulties obtaining access to the associated personal data and technical records.
In my latest update, I informed the Authority of two significant subsequent developments.
First, the volume of unsolicited sexualized emails has continued to increase. Between 10 August and 22 September 2026, I documented 896 unsolicited and harassing emails containing predominantly sexualized material.
I continue to make an important distinction: I do not currently have evidence establishing that the dating-platform operator disclosed my email address, that the unauthorized registration caused these messages, or that all of the messages originate from a common source.
The scale and timing nevertheless make the provenance and recipient information concerning the disputed registration particularly important. I therefore asked the Authority to take this development into account and, insofar as the relevant information exists, to examine whether my email address or other personal data associated with the disputed registration were disclosed or made available to third parties, partners, advertising networks, affiliate systems, or other recipients.
Second, I informed the Authority about the separate Article 15 request of 21 August concerning my controlled test account and the fact that, as of 22 September, I had not received the requested access information.
The controlled account does not establish how the disputed account was created. It provides a comparison point. Because I know the exact circumstances of its creation, the records associated with it may help clarify what registration, session, IP, verification and other technical information the platform normally processes when an account is created without completing email verification.
I have offered to provide the Authority with the relevant correspondence, screenshots, technical information and preserved evidence.
Possible harassment or stalking implications
The continuing volume of unwanted communications also raises a separate question that goes beyond data-protection law.
Austrian criminal law contains provisions concerning persistent harassment (Beharrliche Verfolgung). In particular, § 107a StGB includes, subject to its other legal requirements, conduct involving the use of another person’s personal data in order to cause third parties to make contact with that person.
I am not claiming that this has been established in my case. At present, I do not know whether one person, multiple unrelated actors, automated marketing systems, data brokers, affiliate networks, or some combination of these mechanisms is responsible for the communications I have received.
For that reason, I consider technical attribution essential. The relevant question is not simply that I have received hundreds of unwanted messages, but whether evidence can establish a chain between the unauthorized use of my personal data, particular registrations or disclosures, and subsequent third-party contacts.
The matter therefore remains one of evidence rather than attribution.